Whitehats move 52 bitcoin from the Coldcard hack to a recovery trust
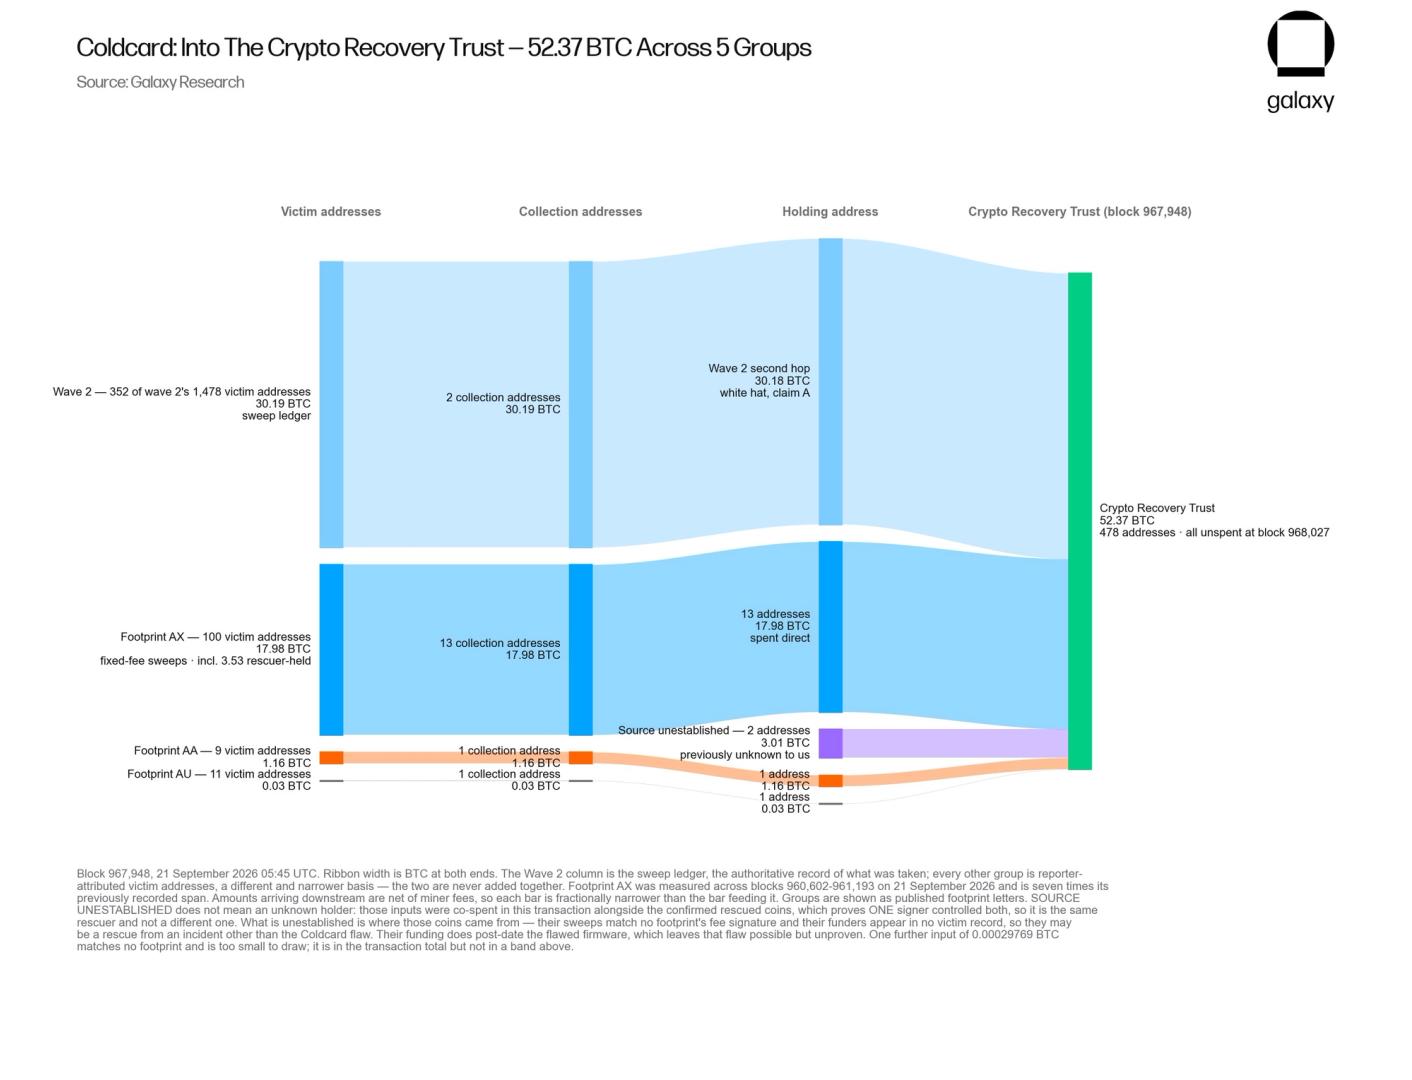
- White-hat hackers moved 52.37 Bitcoin linked to the July Coldcard wallet exploit into an address associated with a newly formed recovery trust.
- The exploit, which caused more than $100 million in estimated losses, used weak software-based randomness to generate wallet seeds that attackers could reconstruct.
- Victims can search their wallet addresses at cryptorecoverytrust.com to determine whether the ethical hackers recovered their funds.
“Whitehat operators” have moved 52.37 BTC to an address linked to a newly formed recovery trust, as part of the ongoing fallout from July's Coldcard hardware wallet exploit, according to Galaxy Digital's Head of Research Alex Thorn.
The Coldcard crypto hardware wallet hack began on July 30, with multiple batches (waves 1, 2, and 3) of attacks in subsequent days resulting in estimated losses of over $100 million in bitcoin
Attackers exploited this, causing wallets to generate seeds using a weaker software-based random number source instead of the wallet’s dedicated random number generator. That made some seeds vulnerable to reconstruction by hackers.
Coinkite, the maker of Coldcard, has since patched the firmware, though funds already exposed under the old seeds remain at risk regardless of the patch.
Read More: Bitcoin cold-wallet attack spreads to 4,500 addresses as losses near $89 million
According to Thorn, some of the coins moved out of victim wallets weren't taken by malicious actors but by whitehats, or ethical cybersecurity professionals who use hacking skills to find and fix security weaknesses.
These so-called good guys swept the funds specifically to keep them safe until they could be returned.