Google AI agents audit Signal’s code and one major flaw stays hidden
Quick Take
- DeepMind reports machine-checked proofs for a compiled Signal library build, with humans choosing the specifications.
- The results cover specified messaging operations under explicit assumptions.
- Public instructions support outside checking, but CryptoSlate has not independently rebuilt and checked the full proof package.

Google DeepMind researchers say their AI agents produced mathematical proofs linking specific security guarantees to a compiled build of Signal’s encryption library, and they put the resulting evidence online for others to check.
The Nov. 10 AlphaProof Code report describes about 6.5 million lines of machine-checked Lean proof code. The result concerns a particular build of libsignal, the Signal protocol’s implementation, under explicit assumptions about cryptography and the environment in which the code runs.
The authors say five people worked on the proofs over four weeks. Humans directed the work, selected reference models and reviewed the specifications that defined what the agents had to prove.
What Google DeepMind's proofs cover
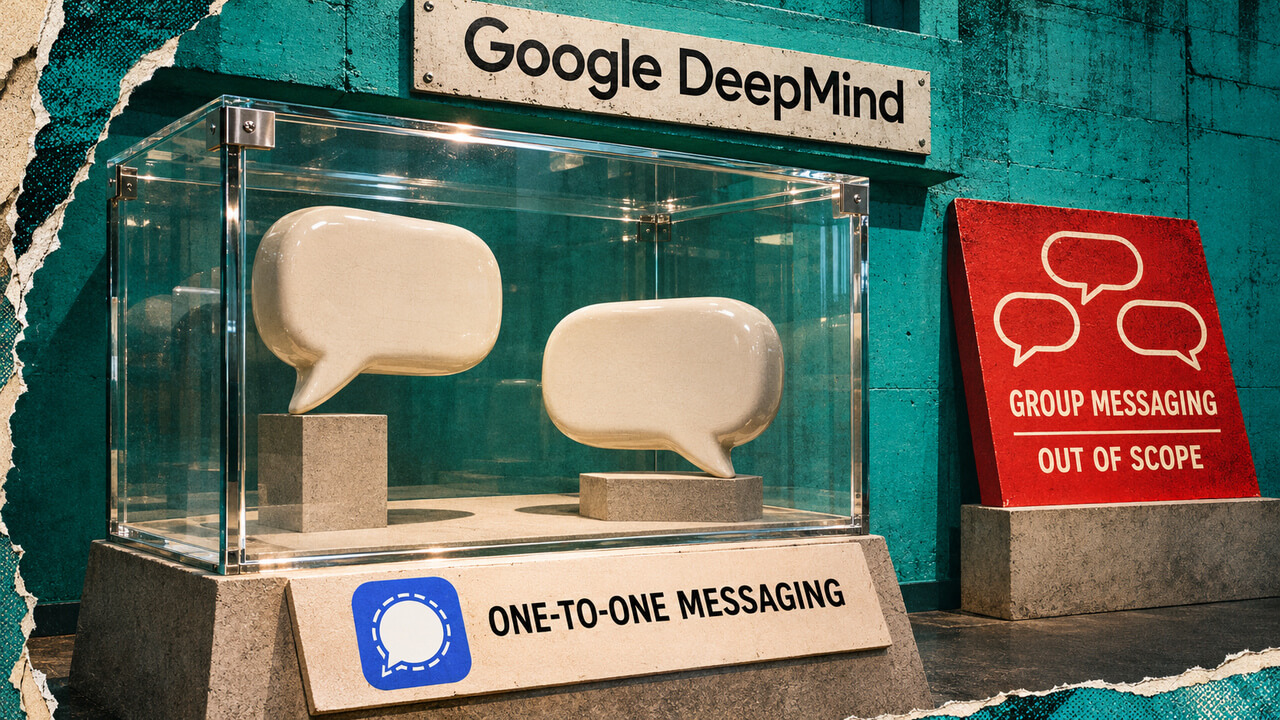
The target was an AArch64 Linux executable using libsignal-protocol v0.105.4 and SPQR v1.6.0 inside a small command-line harness. The theorems cover session initialization, sending a message, and receiving one. Key generation falls outside that verified scope.
The Google report connects the compiled executable to specified properties of PQXDH and Triple Ratchet one-to-one messaging, including forward secrecy, authentication, and post-compromise security.
These address whether earlier messages stay secret after keys are stolen, whether senders are authentic, and whether a session can regain secrecy after a compromise.
Its two proof models provide different assurances: the symbolic analysis relies on idealized cryptographic operations and collision-free executions, while the computational analysis bounds the success of classical attackers under stated cryptographic assumptions.
What a checked Signal proof establishes
DeepMind’s reported process connects human-selected requirements and one executable to a machine-checked proof, with trusted assumptions still defining the result.
A checked proof establishes the stated guarantee for the specified build and model.
Author-reported proofs for a specific AArch64 Linux harness. Specifications, execution model, routine contracts and cryptographic assumptions remain trusted. No direct verification of phone apps, key generation or groups; no independent rebuild performed here.
Sources
Supporting facts
- Reported statement In a technical report dated November 10, 2026, Google DeepMind researchers describe AlphaProof Code, a human-guided multi-agent framework that produced about 6.5 million lines of machine-checked Lean proof code for a compiled libsignal command-line build. [1]
- Reported statement The report says five people worked on the proofs over four weeks, directing agents, selecting reference models and reviewing specifications; the paper lists nine authors. [1]
- Reported statement The report’s verification target is an AArch64 Linux executable built from libsignal-protocol v0.105.4 and SPQR v1.6.0 in a libsignal-cli harness; its theorems cover session initialization, sending and receiving, but not key generation. [1] [2]
- Reported statement The report’s symbolic proof establishes handshake secrecy under specified later Diffie-Hellman breaks, while the computational proof excludes quantum attackers and multi-device state; group messaging is outside the report’s scope. [1]
- Reported statement The authors’ guarantees concern their libsignal-cli build and modeled execution environment, not direct verification of Signal’s complete phone applications. They depend on specifications reviewed by humans, Lean’s checking kernel, the AArch64 Linux model, contracts for selected routines and assumptions about the underlying cryptographic primitives. [1]
- Reported statement The project repository provides instructions to rebuild a pinned binary, check Lean proofs and run a Linux-only comparator that checks theorem statements and their dependent definitions against trusted statements and replays proofs in a fresh kernel. [2]
Method
Source-bound schematic of the reported proof workflow and trust boundary; connectors show logical dependence, not elapsed time or measured security strength.
Scope
Author-reported proofs for a specific AArch64 Linux harness. Specifications, execution model, routine contracts and cryptographic assumptions remain trusted. No direct verification of phone apps, key generation or groups; no independent rebuild performed here.
 CryptoSlate
The symbolic proof establishes handshake secrecy under specified later breaks of Diffie-Hellman, but the computational proof does not cover quantum attackers. Group messaging is outside the report’s scope, and the computational model excludes multi-device state. Its bounds also stop providing a useful guarantee at sufficiently large workloads.
The results still require trust in Lean’s checking kernel, the specifications reviewed by the researchers, the AArch64 Linux model, and contracts describing selected routines.
The project’s Nov. 11 update, merged on GitHub, says ten more library routines were verified, cutting trusted routine hooks from 37 to 27. Those hooks replace execution of selected routines with assumed descriptions of their behavior.
The update retains libsignal v0.105.4 but changes the pinned executable. The newer build verifies the machine code for those ten routines instead of relying on their modeled contracts.
The project repository provides public instructions to rebuild the pinned binary and check its proofs. A Linux-only comparator checks that the theorems and their dependent definitions match trusted statements, then replays proofs in a fresh Lean kernel.
The authors also report reintroducing two previously fixed libsignal bugs and proving that the modified binaries violate their symbolic security theorem. That tests whether the specification rejects those known regressions.
The public package gives other researchers a concrete way to check the claimed connection between security requirements and executable code.
Mentioned in this article
Editorial credits
Also known as "Akiba," Liam Wright is a reporter, podcast producer, and Editor-in-Chief at CryptoSlate. He believes that decentralized technology has the potential to make…
Gino Matos is a law school graduate and a seasoned journalist with six years of experience in the crypto industry. His expertise primarily focuses on the Brazilian blockchain…