Chainalysis breach exposed customer names, emails and company roles
Quick Take
- Chainalysis says an intruder accessed customer names, email addresses, user IDs and organization role labels.
- Chainalysis found no evidence so far of access to investigation content or authentication secrets, with its investigation ongoing.
- Users are urged to scrutinize unexpected authentication prompts and enable two-factor authentication while customer-specific record analysis continues.
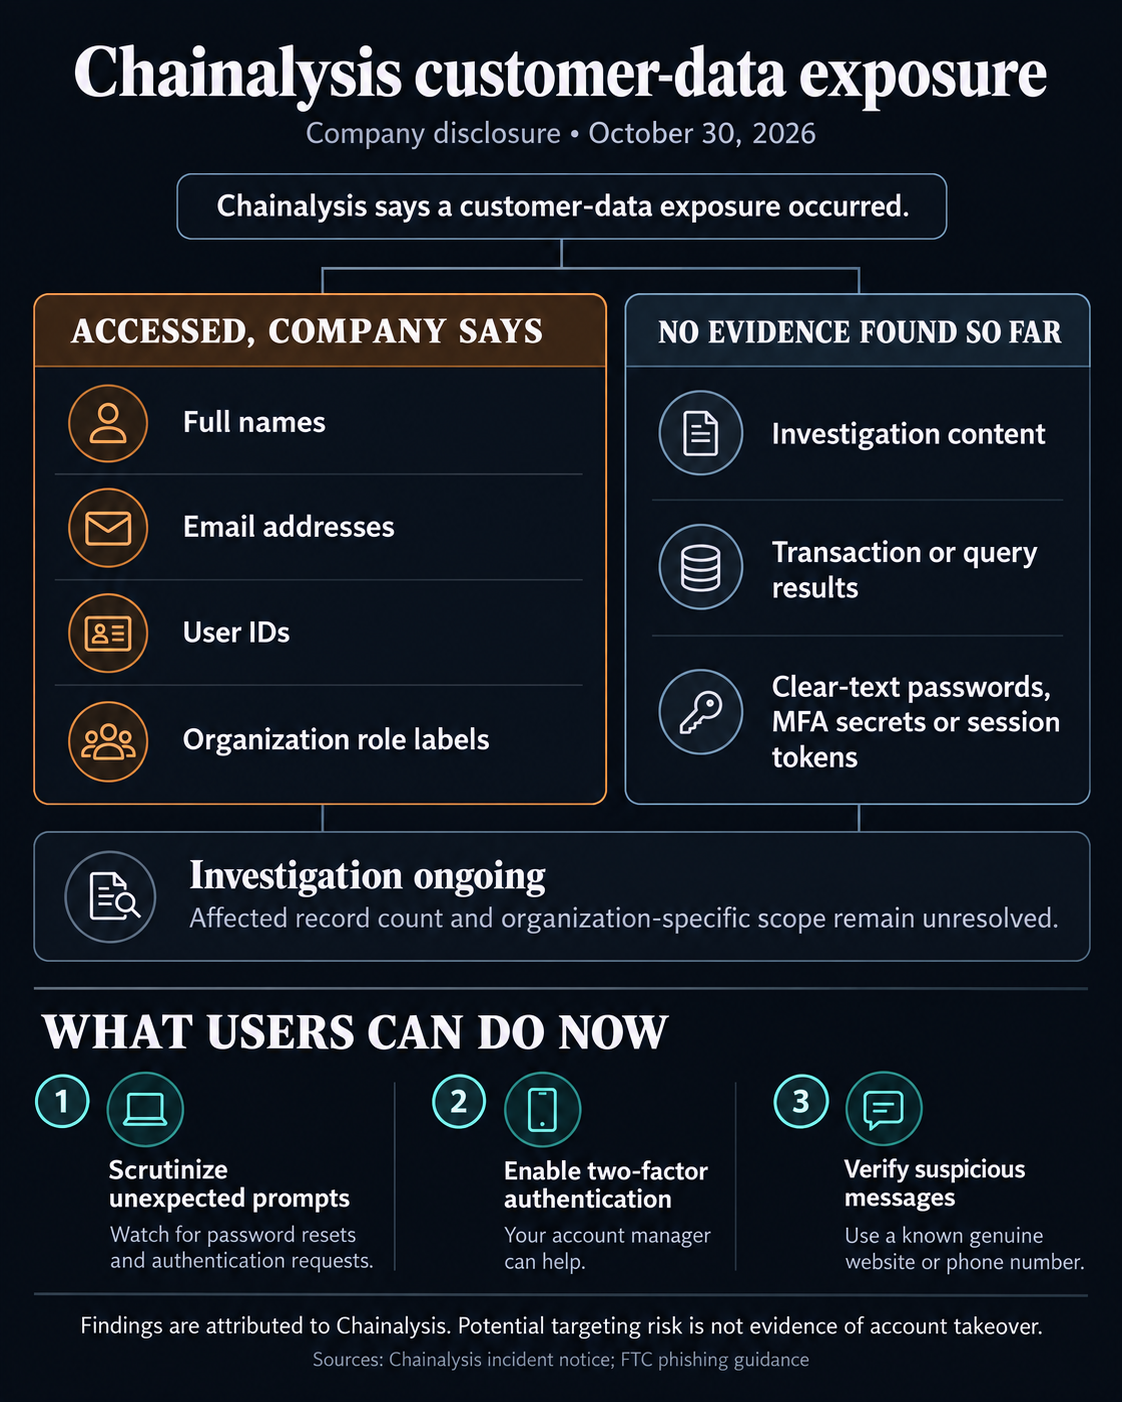
The Chainalysis breach exposed customer names, email addresses, user IDs and organization role labels, the blockchain analytics company said. It urged users to scrutinize unexpected password-reset requests and authentication prompts.
In an Oct. 30 disclosure, the company said it detected an external actor gaining unauthorized access to its systems and internal tools that month. It was still determining which records had been accessed for each affected organization and promised detailed breakdowns when that work was complete.
The disclosure lists data categories without establishing that every listed field was accessed for every user. It did not give an affected-record total, identify the intruder or specify the exploited vulnerabilities. It also said the incident was unrelated to the recent crypto theft involving Binance.
Based on the evidence available at disclosure, Chainalysis said it had found no indication of unauthorized access to investigation content, including graphs, notes or cases; transaction or query results; clear-text passwords; multifactor authentication secrets; or user session tokens. The finding remains provisional while the investigation continues.
Chainalysis said it had notified all customers and engaged third-party cybersecurity experts. Its response included investigating unauthorized activity, patching vulnerabilities and strengthening systems. The company characterized the intruder's methods as “offensive agentic techniques,” but did not provide a technical account explaining how AI was used.
What users can do now
Chainalysis strongly recommended enabling two-factor authentication for organizations that have not already done so, with help available through their account managers. It also urged users to remain especially alert to unexpected password resets and authentication prompts.
Exposed identity information can matter even when passwords are not known to have been accessed. MITRE ATT&CK describes names and email addresses as information adversaries may gather for targeting, potentially helping phishing or attempts to compromise accounts.
For a suspicious message, the Federal Trade Commission recommends contacting the company through a phone number or website already known to be genuine. It also recommends multifactor authentication to make it harder for scammers to access an account if they obtain a username and password.
Chainalysis's separate impersonation guidance warns of look-alike websites, copied branding and unauthorized email addresses, and advises verifying communications through official channels.
Further updates on the Chainalysis breach will include customer-specific record breakdowns, the company said.
Mentioned in this article
Editorial credits
Also known as "Akiba," Liam Wright is a reporter, podcast producer, and Editor-in-Chief at CryptoSlate. He believes that decentralized technology has the potential to make…